Health and Safety
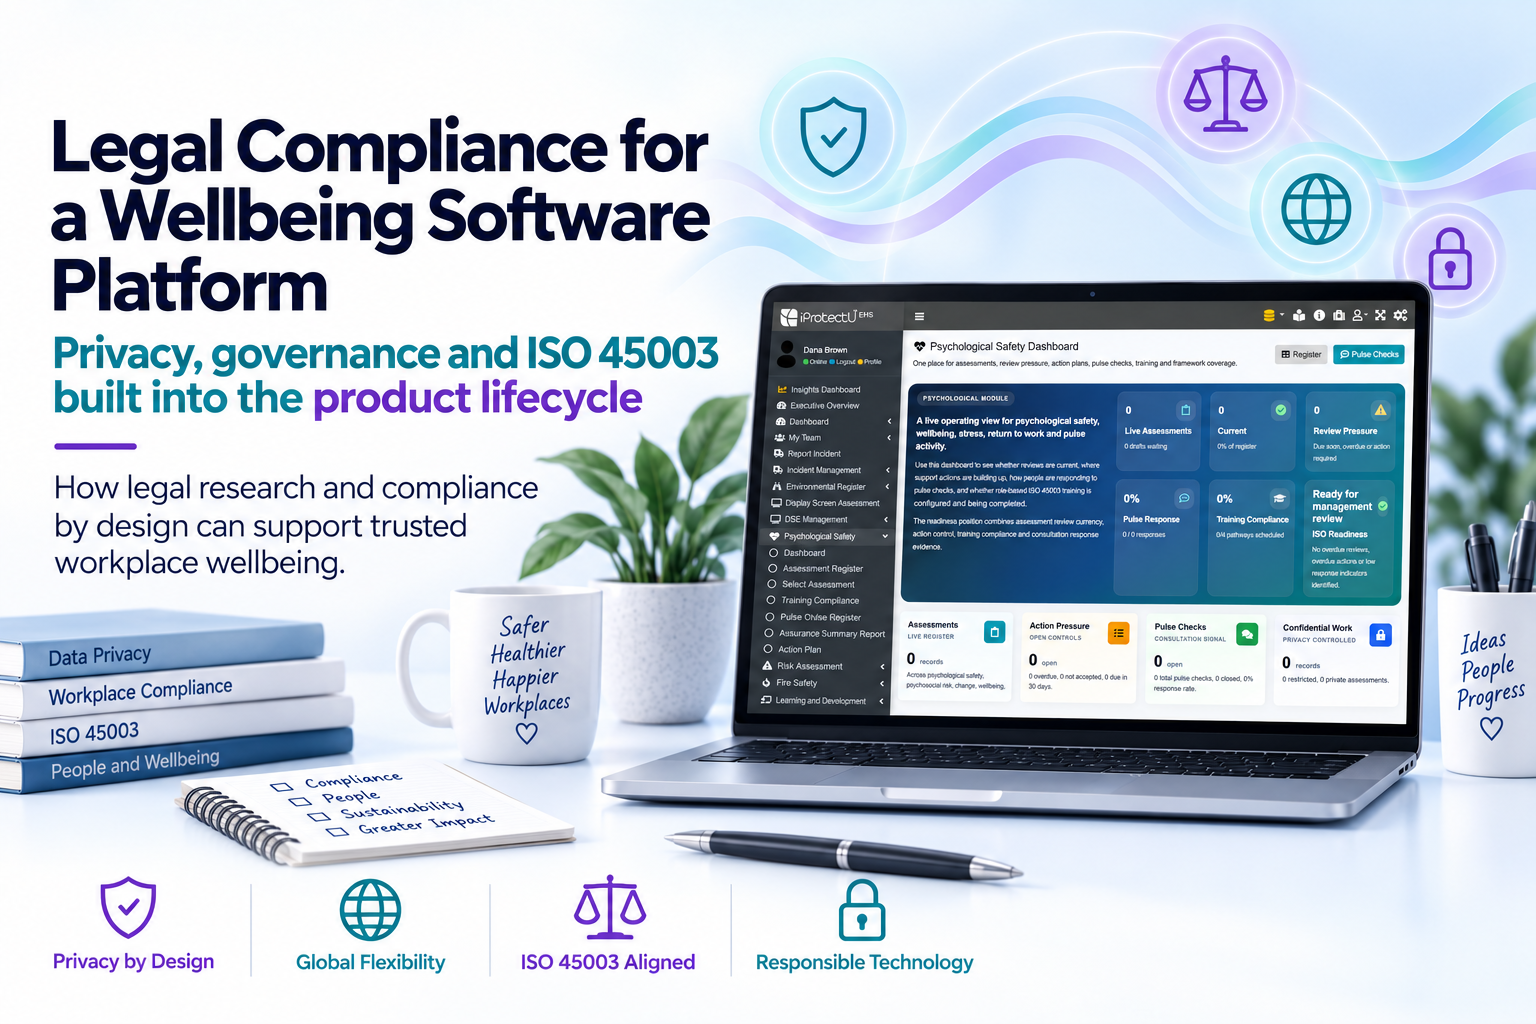
Legal Compliance for a Wellbeing Software Platform
Louis De Maria explains how legal research, privacy by design and ISO 45003 principles helped







Louis De Maria explains how legal research, privacy by design and ISO 45003 principles helped
Christie Richardson explains how market research, product positioning and trust helped bring the iProtectU Wellbeing

Hannah Beck shares how lived experience and inclusive design can help organisations support neurodivergent employees
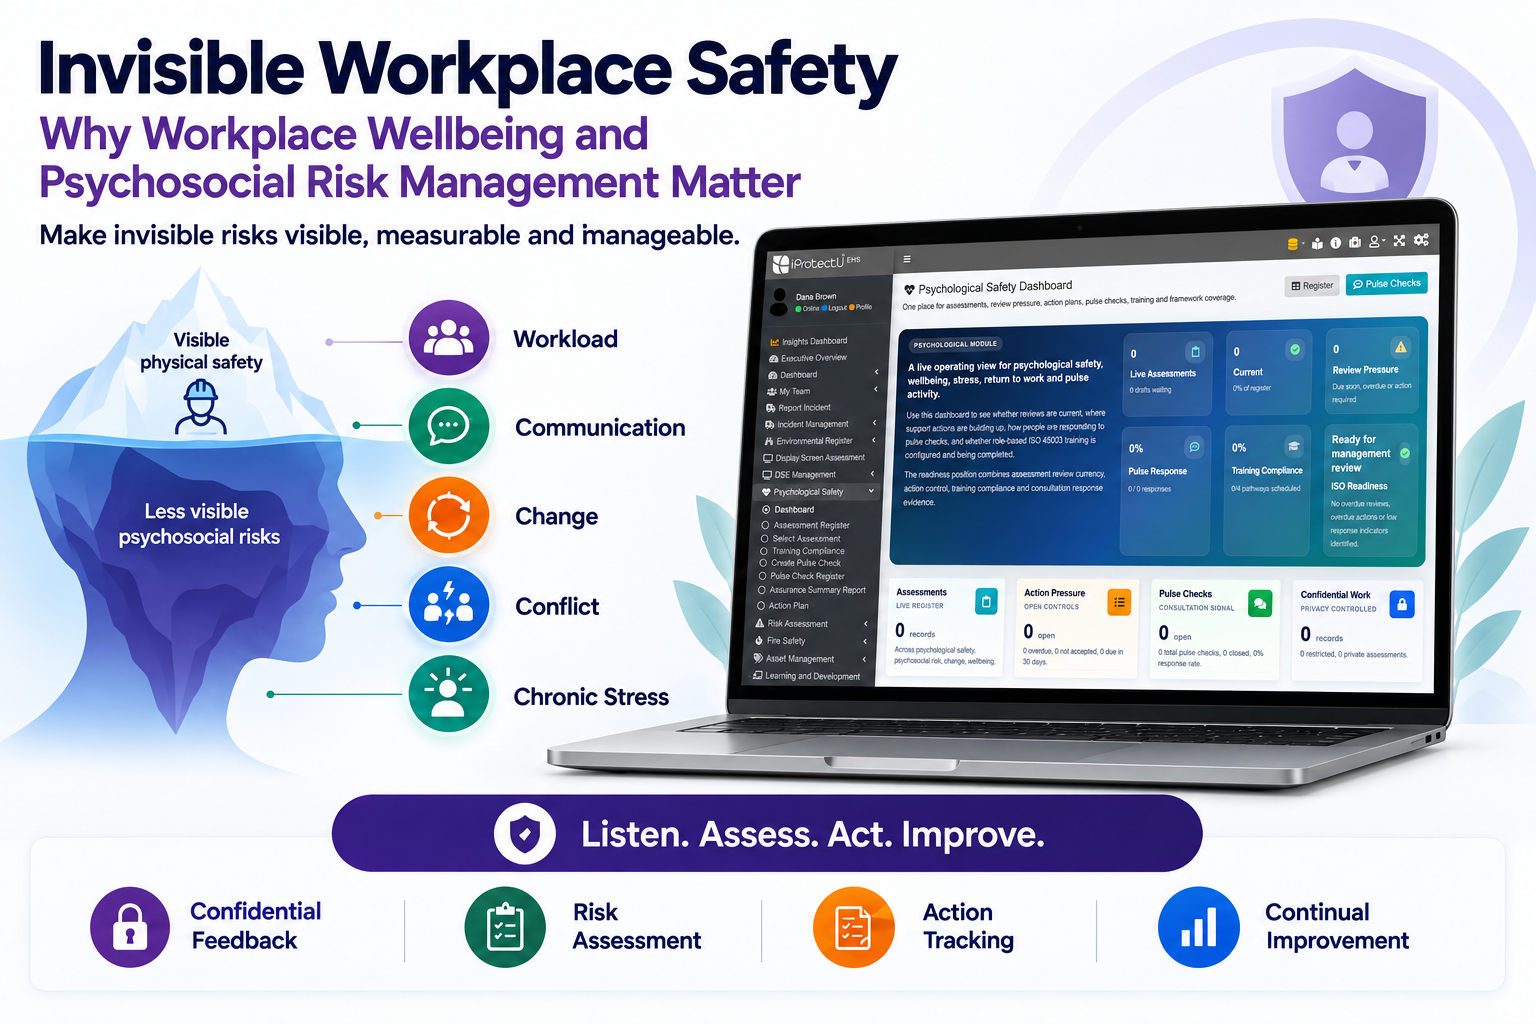
Emily MacLean explores the invisible psychosocial risks affecting workplace wellbeing and how organisations can turn
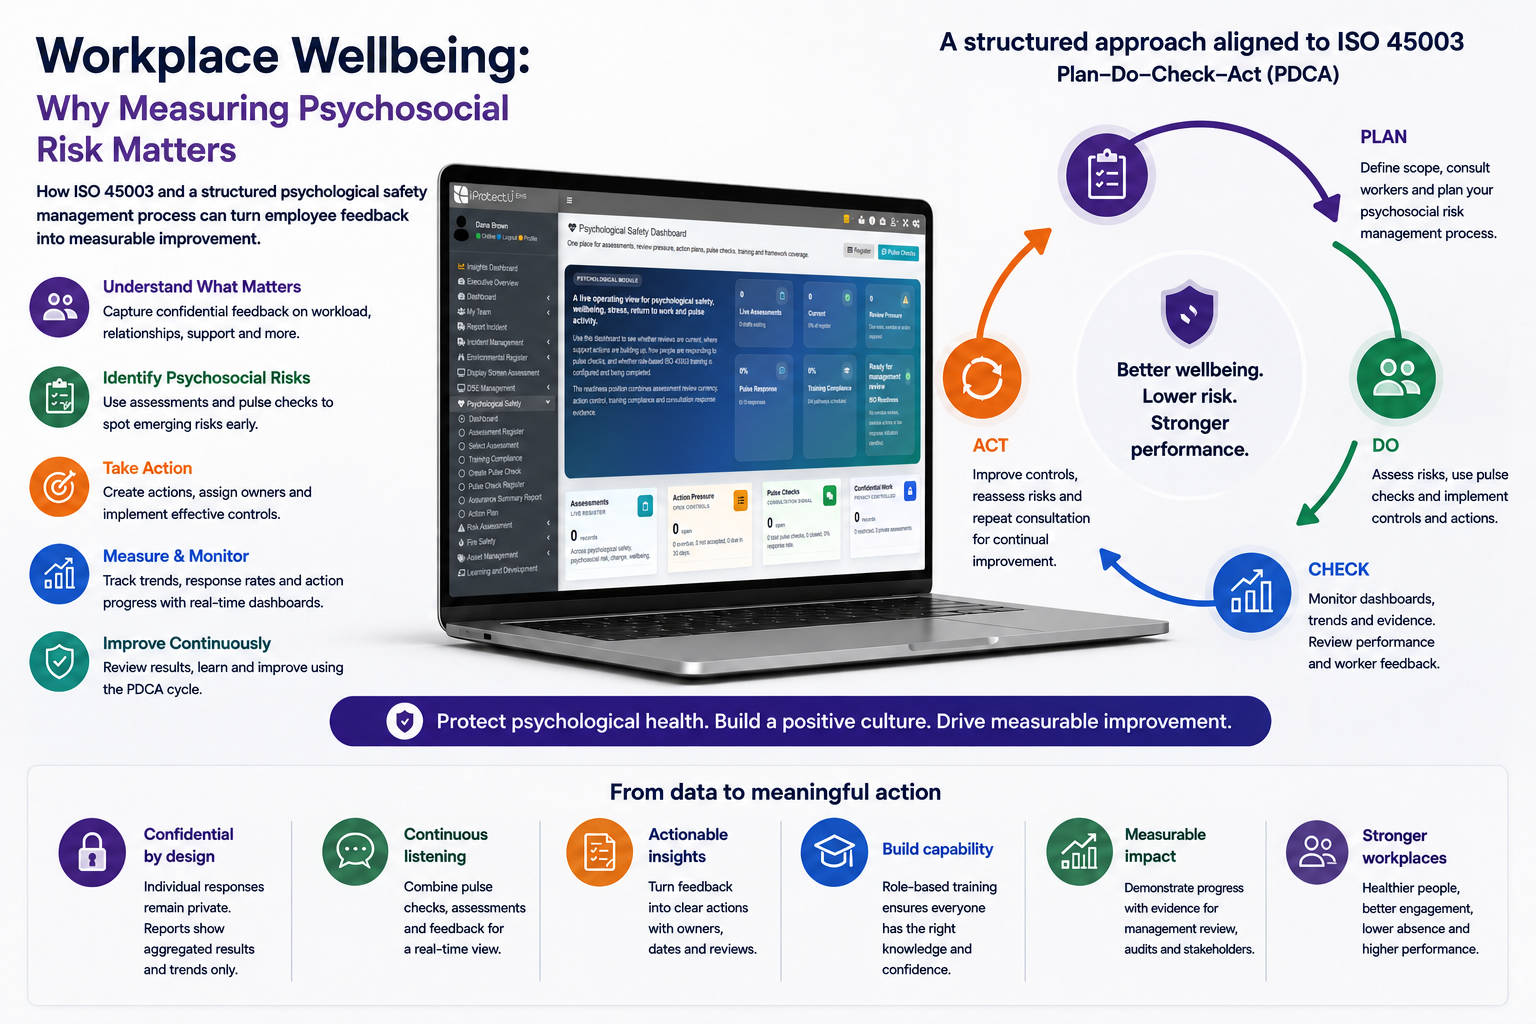
Celeste Weston explains why measuring psychosocial risk helps organisations turn employee feedback into action, improvement
Sophia Berg Merino reflects on helping create a global workplace wellbeing platform shaped by collaboration,